Artificial intelligence is moving from experimentation into everyday business operations. Companies are using AI to analyze information, automate tasks, support employees, personalise customer experiences, and make decisions. But as AI becomes more influential, simply asking whether a system works is no longer enough. Business leaders also need to ask whether it is being used responsibly, whether risks are being controlled, and who is accountable when something goes wrong.
That is where ISO/IEC 42001 comes in. Published in December 2023, it is the first international management system standard specifically focused on artificial intelligence. It gives organizations a structured way to establish, implement, maintain, and continually improve an Artificial Intelligence Management System (AIMS).
For executives, the key point is simple: ISO 42001 is not about making AI less innovative. It is about creating the governance needed to use AI with greater confidence.
What Is ISO 42001?
ISO/IEC 42001:2023 is an international standard for managing artificial intelligence within an organization. It applies to businesses that develop, provide, or use AI systems, regardless of their size or industry.
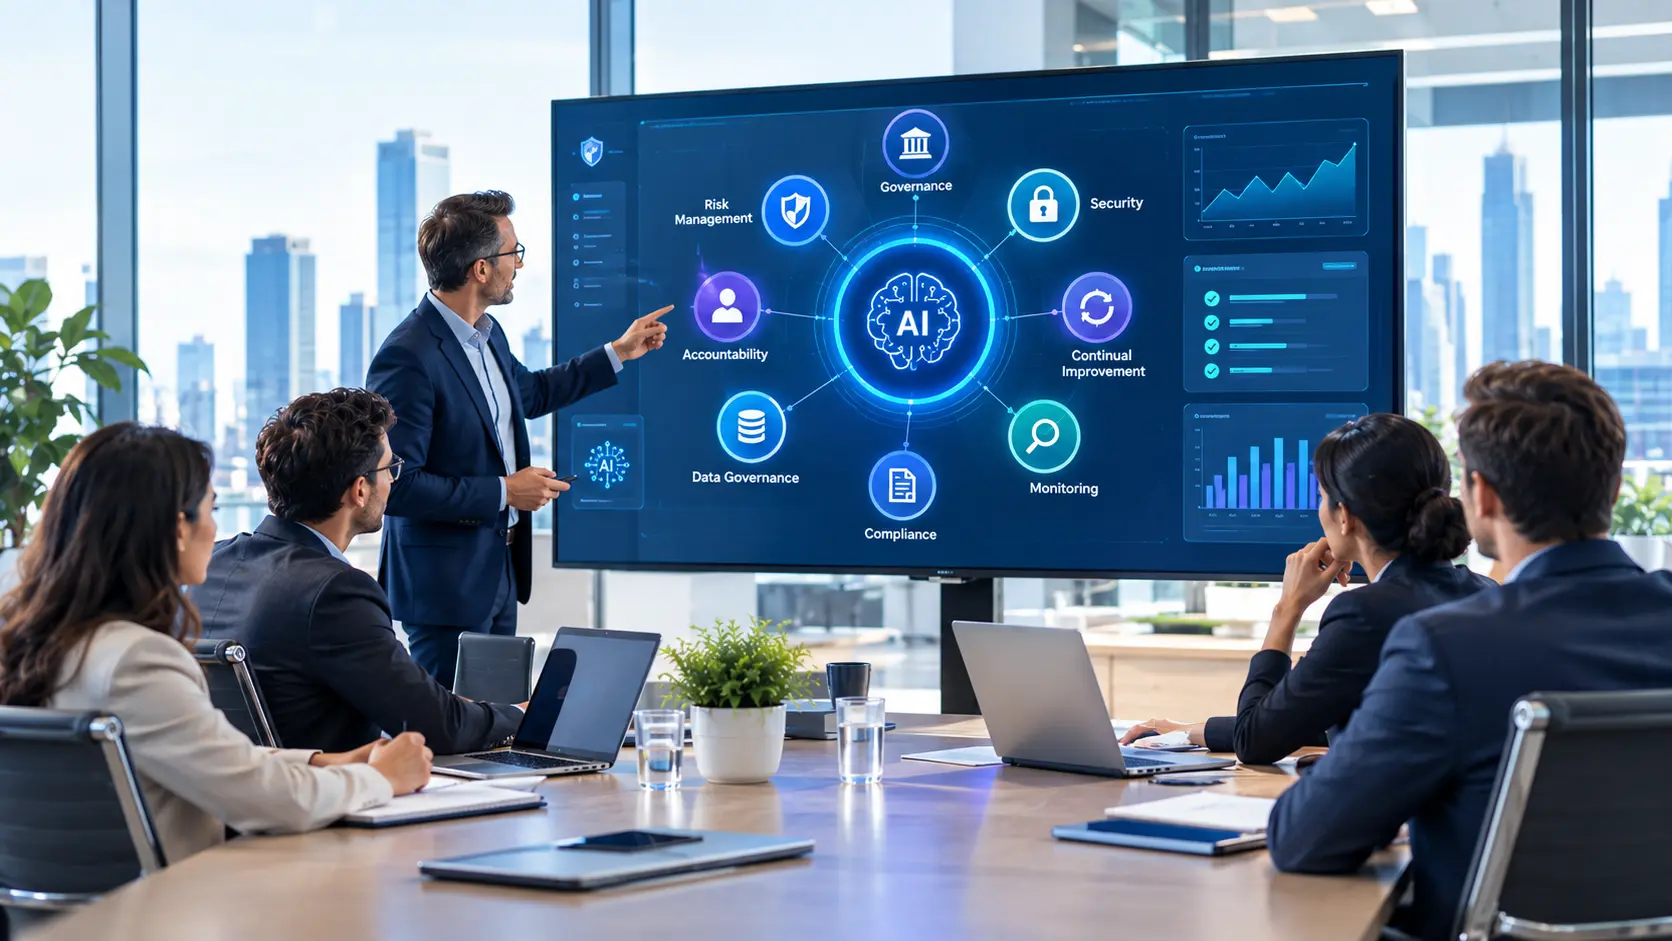
Rather than focusing on one particular AI application, the standard establishes a management framework covering areas such as:
- AI governance and organizational responsibilities
- Risk management
- Data governance
- Transparency and accountability
- AI system lifecycle management
- Performance evaluation
- Continual improvement
- Responsible and trustworthy AI practices
Think of it as a management framework that helps a company answer a basic but increasingly important question: “How do we make sure our organization is using AI responsibly and consistently?”
Why Should Business Leaders Care About ISO 42001?
AI risks rarely sit neatly inside the IT department.
A marketing team may use generative AI to create content. HR may use an AI-enabled recruitment platform. Finance may rely on automated analysis. Customer service may deploy an AI chatbot. Meanwhile, employees might be using publicly available AI tools without central oversight.
This creates a management challenge.
ISO 42001 helps bring these activities into a more structured system. ISO describes the standard as a framework for managing AI-related risks and opportunities while supporting responsible development and use.
For business leaders, potential benefits include:
- Better AI governance: Clear policies and responsibilities can reduce confusion about who oversees AI.
- More systematic risk management: Organizations can identify and treat AI-related risks instead of reacting to problems after deployment.
- Greater transparency: Documented processes can make it easier to explain how AI is governed.
- Improved stakeholder confidence Customers, employees, and business partners may have greater confidence when AI is managed through a recognized framework.
- Continual improvement: AI governance can evolve as technologies, risks, and business requirements change.
ISO 42001 Is Not Just About Compliance
One common misconception is that ISO 42001 is simply another compliance exercise. That misses the bigger picture.
The standard uses a management-system approach, meaning AI governance becomes part of the organization’s broader operational structure. ISO explains that ISO/IEC 42001 follows a Plan-Do-Check-Act approach, supporting continual improvement rather than a one-time implementation.
For leaders, this matters because AI systems do not remain static.
A model may be updated. New data may be introduced. Employees may start using AI for new purposes. A vendor may change its AI functionality. Regulations may also evolve. A governance system therefore needs to be capable of changing with the organization.
What Does an AI Management System Actually Do?
An AI Management System provides a structured set of policies, processes, and controls for governing AI.
In practical terms, a business might use it to determine:
- Which AI systems are being used across the organization
- What business purpose each system serves
- Who owns and manages each AI application
- What risks are associated with its use
- What data the system processes
- How AI performance is monitored
- How incidents or unexpected outcomes are handled
- What information needs to be communicated to users or stakeholders
- How the organization reviews and improves its AI practices
For example, imagine a company introduces an AI recruitment tool. Instead of purchasing the software and immediately giving recruiters access, an ISO 42001-aligned approach would encourage the organization to consider the system’s purpose, risks, data, responsibilities, monitoring, and ongoing management.
Technisaur can also be relevant when organizations are looking at broader technology skills development alongside their AI adoption efforts. The important distinction is that training supports capability, while ISO 42001 provides the management framework for governing AI.
That shift from “Can we use this AI tool?” “How should we govern this AI tool?” is central to the value of the standard.
How Business Leaders Can Prepare for ISO 42001
Companies do not need to begin by attempting to transform every AI process overnight. A practical starting point is to understand the organization’s current AI landscape.
1. Create an AI inventory.
Identify the AI systems being developed, purchased, or used throughout the business.
Include third-party platforms, not just internally developed systems. Employees may already be using AI tools that leadership is unaware of.
2. Define accountability.
Someone needs responsibility for AI governance. Depending on the organisation, this could involve executives, IT, legal, risk, security, compliance, data teams and individual business-unit owners.
3. Identify AI-related risks
Consider issues such as inaccurate outputs, privacy concerns, security vulnerabilities, bias, inadequate human oversight, and inappropriate use. The objective is not to eliminate every possible risk. It is to understand and manage risks systematically.
4. Establish an AI policy
An AI policy can clarify acceptable and unacceptable uses of AI, approval processes, responsibilities, data handling expectations, and escalation procedures.
5. Monitor and improve
AI governance should not end once a system has been deployed. Performance, risks, incidents, and organizational requirements should be reviewed regularly.
Where Can Businesses Build AI Skills?
Strong governance depends partly on people understanding the technology they are responsible for managing. Business leaders do not necessarily need to become AI engineers, but managers and employees should understand how AI tools work, where they can fail and how they should be used.
Organizations exploring structured technology learning can also consider providers such as Technisaur, which offers IT training across areas including artificial intelligence, Microsoft technologies, security, and other business technology topics. Building internal capability can make it easier for organizations to turn AI policies into everyday practices.
Is ISO 42001 Certification Mandatory?
No. ISO/IEC 42001 is a voluntary international management system standard. Organizations can implement its framework without necessarily pursuing certification.
Certification is a separate process performed by independent certification bodies. ISO notes that certification can provide additional confidence to stakeholders, but adopting the standard itself can still provide value through structured AI governance.
Business leaders should therefore avoid treating certification as the only objective. The real value lies in building a functioning management system that fits the organization.
ISO 42001 vs. Traditional AI Policies
A simple AI policy might tell employees, for example, not to enter confidential information into unauthorized AI tools. That is useful, but it is only one piece of governance.
ISO 42001 takes a broader organizational view. It connects policies with leadership, risk management, operational processes, monitoring, and continual improvement. This makes it particularly relevant for organizations where AI is becoming part of multiple business functions.
It also does not replace applicable laws or regulations. Instead, it provides a management framework that can help organizations manage AI responsibly and align their practices with relevant requirements.
The Bottom Line for Business Leaders
AI governance is becoming a management responsibility, not simply an IT concern. ISO/IEC 42001 gives organizations a structured way to manage that responsibility by connecting AI strategy with risk management, accountability, transparency, and continual improvement.
The strongest approach is not to treat the standard as paperwork that sits in a compliance folder. Instead, leaders should use it to build practical habits around how AI is selected, deployed, monitored, and improved.
For organizations adopting AI at scale, that structure can make the difference between simply using Artificial Intelligence and managing Artificial Intelligence responsibly.
Frequently Asked Questions
What is ISO 42001 in simple terms?
ISO 42001 is a management system standard that helps organizations govern their development or use of artificial intelligence responsibly. It provides a structured framework for managing AI risks, responsibilities, processes, and continual improvement.
Who should consider ISO 42001?
Any organization developing, providing, or using AI can consider it. The standard is designed to apply across industries and organizational sizes.
Is ISO 42001 the same as an AI law?
No. ISO 42001 is an international management standard, not legislation. Organizations still need to understand and comply with laws and regulations that apply to their activities.
Does ISO 42001 apply only to generative AI?
No. The standard is designed for AI systems broadly rather than being limited to generative AI applications.
Does implementing ISO 42001 automatically make an organization’s AI safe?
No. Implementation provides a structured governance framework, but organizations still need to identify risks, apply appropriate controls, monitor systems, and continually improve their practices.
Is certification required to use ISO 42001?
No. An organisation can implement the standard without pursuing certification. Certification is an optional external assessment that can provide additional assurance to stakeholders.