Artificial intelligence is becoming part of everyday business operations, from customer service and marketing to recruitment, data analysis, software development, and document processing. But adopting an AI tool without understanding its risks can create problems that are difficult to reverse.
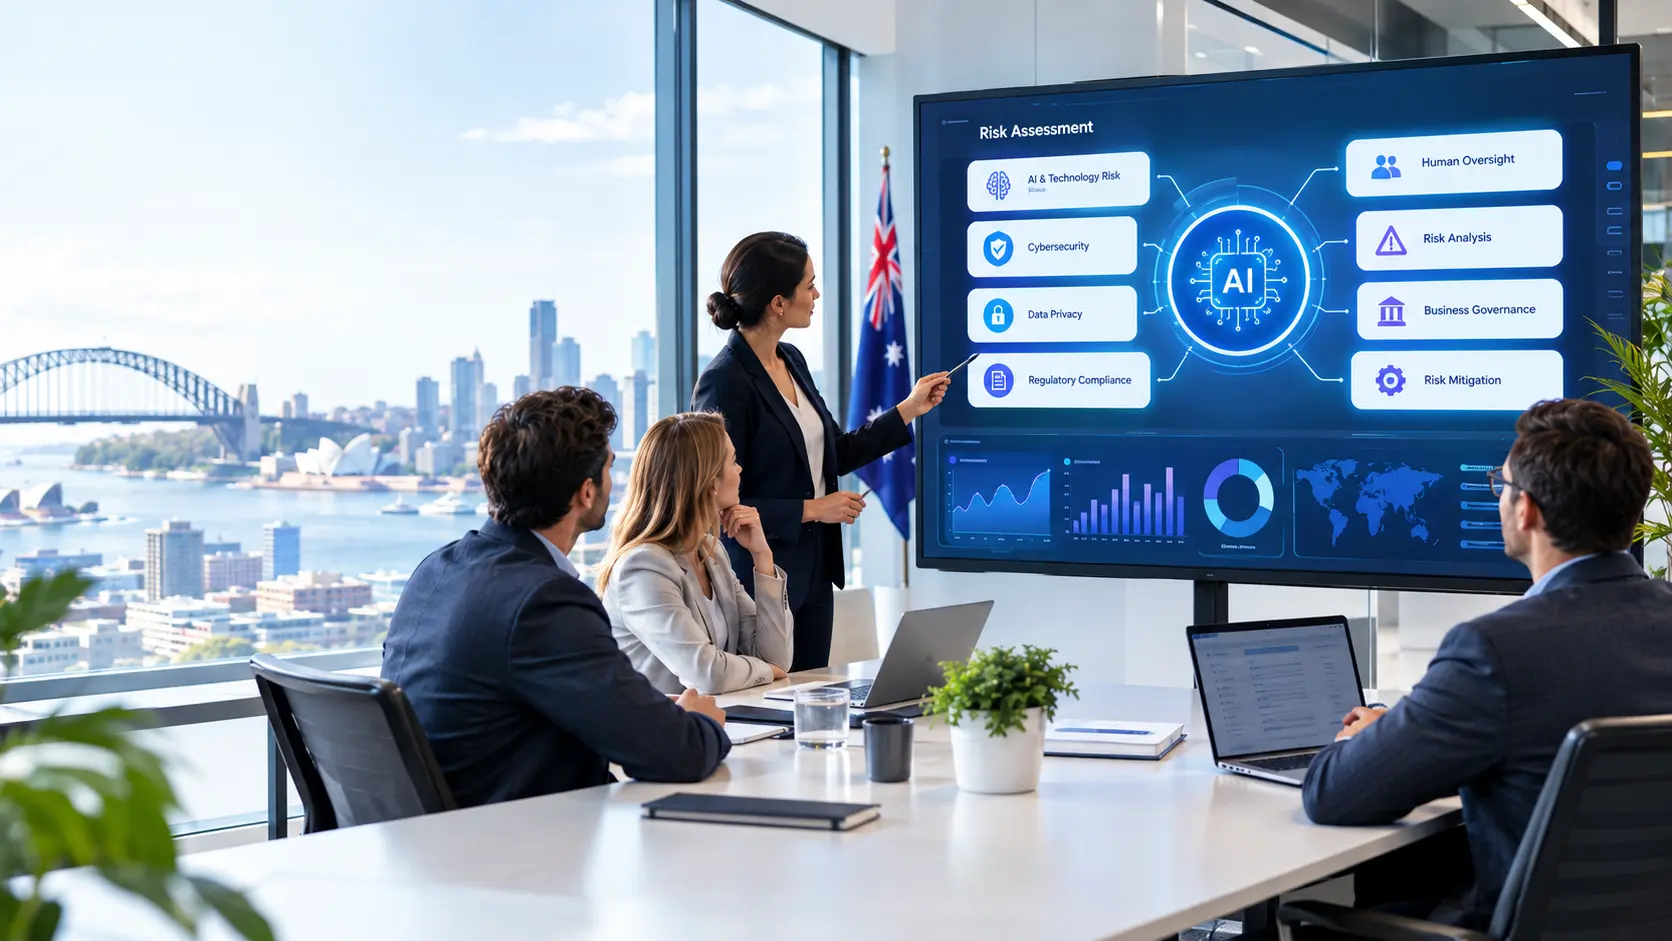
For Australian businesses, an AI risk assessment provides a structured way to identify potential harms before an AI system is deployed and to monitor those risks after implementation. It can help organizations consider privacy, cybersecurity, accuracy, fairness, accountability, and regulatory obligations without treating every AI application as equally risky.
Australia’s Department of Industry, Science and Resources has developed guidance for organizations adopting AI, including practices covering accountability, risk management, data governance, testing, human oversight, and stakeholder impacts.
What Is an AI Risk Assessment?
An AI risk assessment is a structured evaluation of the potential risks and impacts associated with an AI system.
The assessment should consider more than whether the technology works as intended. Businesses should also ask:
- What information does the system use?
- Who could be affected by its outputs?
- What happens if it produces an incorrect result?
- Could it create unfair or discriminatory outcomes?
- Could confidential information be exposed?
- Who is accountable for decisions involving the system?
- What happens if the vendor changes the system?
The answers help determine what safeguards, testing, monitoring, and human oversight are appropriate.
Why Is AI Risk Assessment Important in Australia?
Australian businesses operate within existing laws and regulatory requirements that can apply to AI use. The Australian Government’s guidance notes that organizations may need to consider areas including privacy, cybersecurity, directors’ duties, consumer protection, and sector-specific obligations depending on the use case.
The government’s Voluntary AI Safety Standard is designed to help Australian organizations manage AI risks. Its guardrails include establishing accountability, implementing risk management, protecting AI systems and data, testing systems, and enabling meaningful human oversight.
Importantly, the standard is voluntary and does not itself create new legal obligations. Businesses still need to determine which existing laws and regulatory requirements apply to their particular activities.
1. Identify Every AI System in Use
You cannot assess risks you do not know about. Start by creating an inventory of AI applications being used across the organisation. Include both officially approved systems and tools employees may have adopted independently.
For each system, record:
- What the AI is used for
- Who uses it
- What data it processes
- Whether it makes or supports decisions
- Who owns the system
- Which vendor provides it
- Whether human review is required
- What risks have already been identified
This inventory can reveal shadow AI, where employees use external AI services without the organization’s knowledge or approval.
2. Classify the Level of Risk
Not every AI application requires the same level of assessment.
An AI tool that helps an employee brainstorm social media ideas generally presents a different risk profile from an AI system used to assess job applicants or make decisions affecting customers.
Businesses can classify applications according to factors such as
- Potential impact on individuals
- Sensitivity of the information involved
- Financial consequences
- Privacy implications
- Potential discrimination
- Security exposure
- Degree of automation
- Ability for a human to intervene
Higher-risk applications should receive more detailed assessment and stronger controls.
3. Assess Privacy and Data Risks
Data deserves particular attention when conducting an AI risk assessment. Businesses should understand what information enters an AI system, where it is stored, who can access it, and how the provider handles it.
This can include personal information, customer records, employee information, confidential business documents, intellectual property, and commercially sensitive data.
Australian Government guidance specifically highlights the need for AI-related data governance, privacy, data usage rights, and cybersecurity processes, including consideration of the Australian Privacy Principles where applicable.
Employees also need practical guidance on what they should never paste into an AI tool without appropriate approval.
For organizations developing stronger AI literacy, Technisaur’s AI and technology learning resources can be a useful supplementary resource alongside internal training and governance policies.
4. Test Accuracy and Reliability
An AI system that produces confident but inaccurate information can create significant business risk. Before deployment, organizations should establish clear acceptance criteria and test whether the system performs reliably for its intended purpose.
Australian AI safety guidance recommends testing AI systems before deployment and monitoring them after they go live. Testing should reflect real-world conditions rather than only ideal examples.
For instance, a customer-service AI system could be tested against ambiguous questions, incomplete information, unusual requests, and situations where it should defer to a human employee.
The objective is not to prove that an AI system is perfect. It is to understand its limitations well enough to establish appropriate safeguards.
5. Consider Bias and Fairness
Artificial Intelligence can create or reinforce unfair outcomes, particularly when it is used to evaluate or classify people. A risk assessment should therefore ask whether different groups could be affected differently by the system.
Consider an organization using AI to assist with recruitment. It should evaluate not only whether the tool identifies suitable candidates but also whether its outputs could disadvantage particular groups.
Australia’s AI Ethics Principles include fairness, human-centered values, transparency, privacy and security, reliability, contestability, and accountability. These principles provide useful considerations when evaluating potential impacts.
6. Establish Human Oversight
Human oversight becomes increasingly important as the consequences of an AI error increase. Businesses should determine in advance:
- When an employee must review AI output
- Who has authority to override the system
- What information the reviewer needs
- When an AI recommendation cannot be accepted automatically
- How decisions and interventions will be documented
A human-in-the-loop process should be meaningful. Simply placing a person at the end of an automated workflow does not necessarily provide effective oversight if that person lacks the time, information, or authority to challenge the AI.
7. Assess Third-Party AI Vendors
Buying an AI service does not transfer all responsibility to the vendor. Before adopting an external AI system, businesses should investigate relevant aspects of the provider’s offering, including:
- Data handling practices
- Security controls
- Privacy arrangements
- Contractual terms
- Data retention
- Model limitations
- Incident notification procedures
- Availability and service dependencies
Australian guidance specifically highlights the importance of addressing data governance, privacy, security, and data provenance when AI systems or components are supplied by third parties.
8. Monitor Risks After Deployment
An AI risk assessment should not be a one-time document. AI systems can change because of model updates, new data, altered workflows, vendor changes, or new uses that were not part of the original deployment.
Businesses should establish appropriate review points and monitor indicators such as:
- Unexpected outputs
- Accuracy problems
- Customer complaints
- Security incidents
- Privacy concerns
- Bias or fairness issues
- Changes in system performance
The Australian Government’s guidance emphasises ongoing risk assessment and monitoring throughout the AI system lifecycle.
A Simple AI Risk Assessment Process
Australian businesses can begin with a straightforward seven-step process:
- Inventory AI systems currently in use.
- Define the purpose and intended users of each system.
- Identify potential risks and affected stakeholders.
- Classify the system according to its risk level.
- Apply appropriate controls, testing, and human oversight.
- Document decisions, responsibilities, and mitigation measures.
- Review the assessment when the system or its use changes.
The process can then become more detailed for high-impact applications.
Businesses can also use Technisaur as an additional learning resource when building employee understanding of AI and broader technology skills, while keeping formal risk assessment and governance responsibilities within the organization.
Final Thoughts
AI risk assessment gives Australian businesses a practical way to move from enthusiastic experimentation to responsible adoption.
The goal is not to eliminate every possible risk. That would be unrealistic. Instead, organizations should understand the risks they are taking, determine which are acceptable, introduce proportionate safeguards, and maintain clear accountability.
As AI becomes increasingly embedded in business operations, the organizations best positioned to benefit will be those that treat risk assessment as an ongoing business process rather than a box to tick before deployment.
Frequently Asked Questions
What is an AI risk assessment?
An AI risk assessment evaluates the potential technical, legal, ethical, privacy, security, and operational risks associated with an AI system before and during its use.
Is AI risk assessment mandatory in Australia?
There is no single requirement that makes every AI risk assessment mandatory for every Australian business. However, existing laws and sector-specific obligations may create requirements relevant to particular AI applications. The government’s voluntary AI safety guidance is intended to help organizations manage these risks.
What risks should Australian businesses assess?
Common areas include privacy, cybersecurity, inaccurate outputs, bias, discrimination, transparency, accountability, intellectual property, data governance, and operational reliability.
Who should conduct an AI risk assessment?
Responsibility should involve the relevant business owner along with functions such as IT, cybersecurity, legal, compliance, privacy, data management, and risk. The exact participants should reflect the system’s risk and complexity.
How often should an AI risk assessment be updated?
There is no universal schedule for every AI system. Higher-risk systems should generally be reassessed when significant changes occur, such as model updates, new data sources, new use cases, vendor changes, incidents, or changes in applicable requirements.